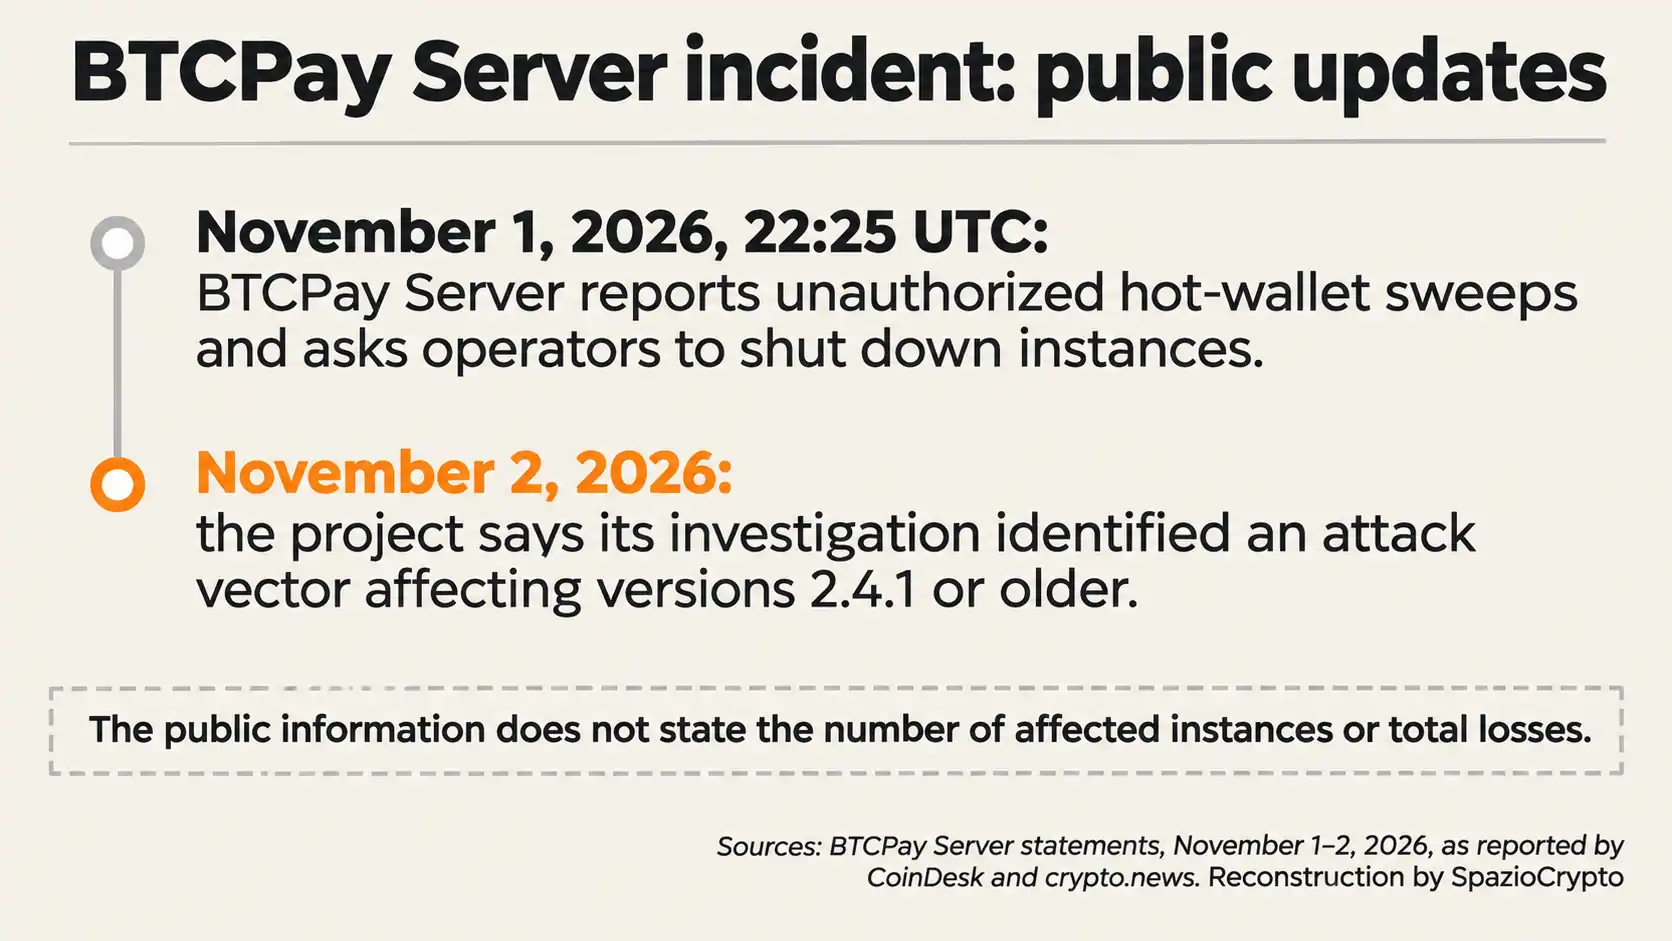
BTCPay Server has urged operators to shut down their instances after receiving reports of hot wallets drained by unauthorized attackers. The warning was published on X on November 1 at 22:25 UTC, instructing operators to run ./btcpay-down.sh to halt the service while the investigation continues.
🚨 We are receiving reports of hot wallets on BTCPay Servers being swept by unauthorized attackers.
— BTCPay Server (@BtcpayServer) November 1, 2026
If you're running an instance, please shut it down (./btcpay-down.sh) until we complete the investigation.
On November 2, the team published a first update: investigators had identified an attack vector tied to version 2.4.1 and earlier. As reported by Crypto.news, the project had not received credible reports of hot wallets being drained on installations running version 2.4.7. That is a preliminary signal, not a definitive finding: it does not yet identify the specific technical flaw, nor does it confirm that all later versions are safe.
What Is Known So Far
BTCPay Server founder Nicolas Dorier stated that, in the incidents examined, attackers had gained administrative access to the affected servers. How they obtained that access remains unknown. The project has not disclosed how many operators were hit or the total value of funds stolen.
The initial alert applied to all operators and did not specify vulnerable versions or a patch. The November 2 update narrowed suspicion to version 2.4.1 and earlier, but the technical root cause has not been described and no fix specific to this incident has been announced.
BTCPay Server is an open-source, self-hosted payment processor that lets merchants and services accept Bitcoin while controlling their own infrastructure. In certain configurations, a hot wallet stores the signing credentials directly on the server: if the server is compromised, any connected funds are exposed. The actual custody risk depends on how each operator has configured their setup.
The incident is therefore limited to the specific installations and wallets named in the reports. Available public information does not indicate that the Bitcoin network itself, or all BTCPay Server deployments broadly, have been compromised.
What Still Needs Answering
The investigation has not yet established the number of affected instances, total losses, or the precise path attackers used to gain administrative privileges. The full scope of the vulnerability relative to versions newer than 2.4.1 also requires further clarification from the project team.
For operators right now, the most concrete guidance is the version indicator published on November 2, alongside the original instruction to shut down instances during the investigation. Official follow-up advisories and any technical details the BTCPay team releases will determine when, and under what conditions, servers can safely return to operation. Operators running version 2.4.7 or later should monitor the project's official channels closely and avoid re-enabling hot wallets until a formal all-clear is issued.