Bitget has revised its estimate of stolen funds from the September 24 hack upward to $387.5 million and published a precise schedule for the gradual reopening of withdrawals beginning September 28. At the same time, the attacker has started moving a substantial portion of the stolen XRP, roughly $83 million worth, exposing a structural limitation that Ripple cannot fix with a simple technical intervention. The Bitget $387.5 million hack is no longer just a story about a single breach: it now offers a real-time window into recovery efforts, withdrawal timelines, and on-chain asset movement simultaneously.
Three developments stand out. Below, they are separated clearly, with a distinction drawn between what has been officially confirmed and what remains unverified, particularly on the question of attribution.
The Stolen Amount Rises to $387.5 Million
Bitget explained that the roughly $35.9 million increase from the initial estimate of $351.6 million does not reflect a second attack. According to the exchange, the higher figure results from the inclusion of transfers on Zcash and TRON that were initially left out of the incident accounting. Bitget maintains this is a more complete reconstruction of the same September 24 event, not a separate or subsequent breach.
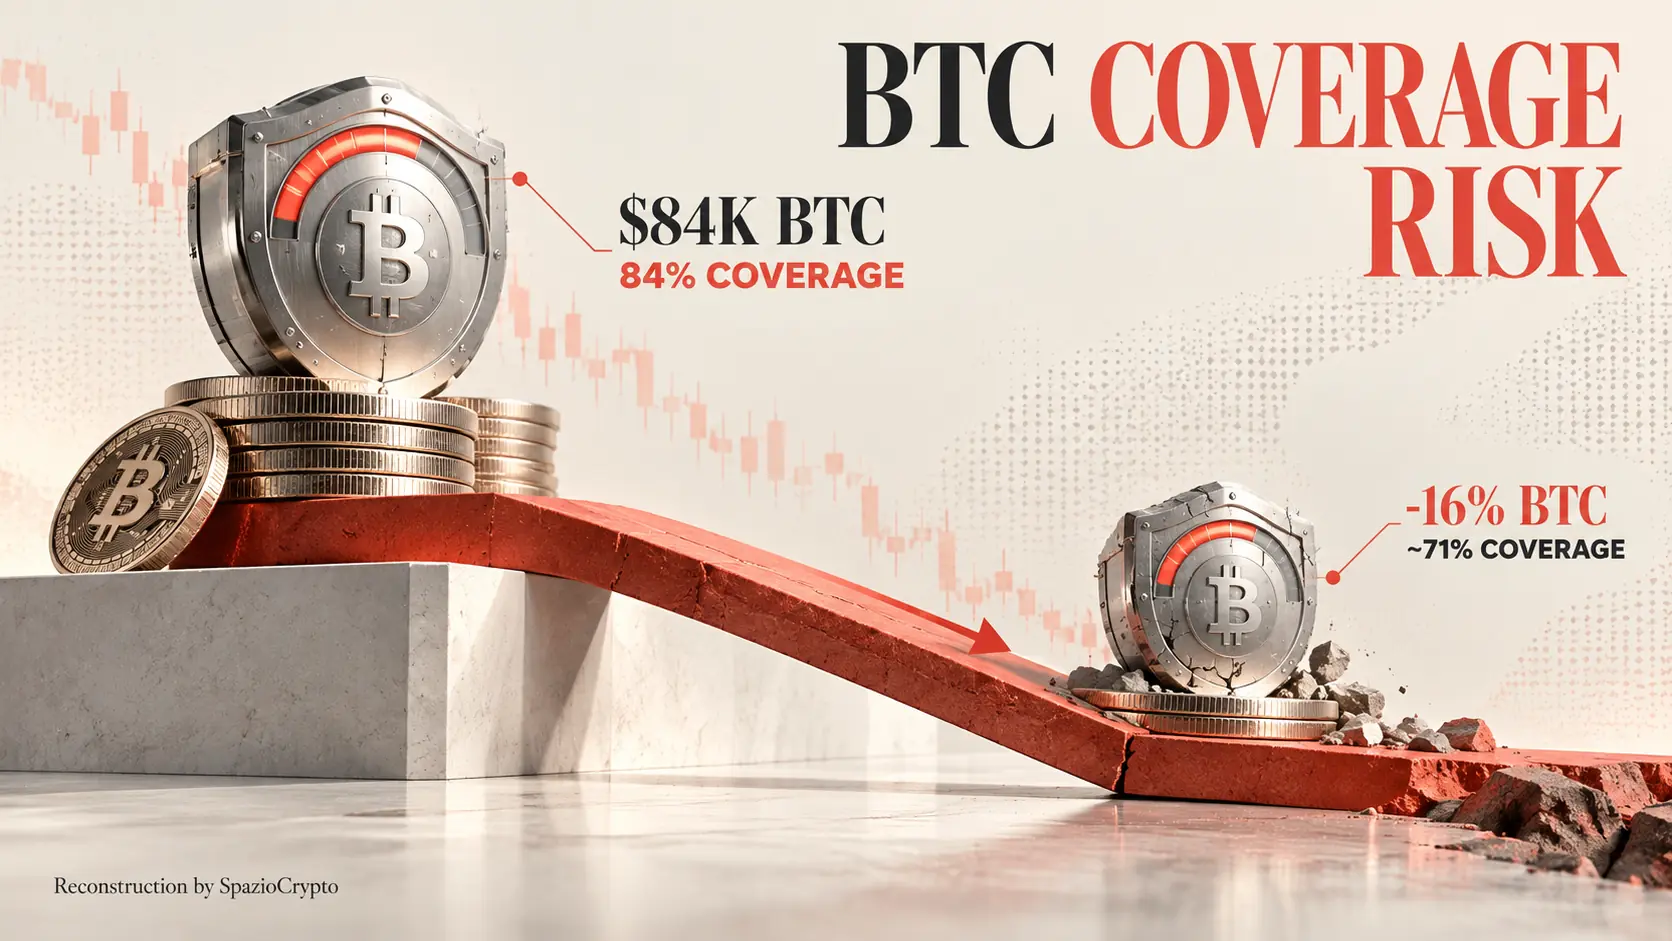
On the recovery side, the exchange has launched a bounty program offering up to 10% of any recovered value, split equally between contributors who help freeze the attacker’s funds and those who assist in actual recovery. The program is open to other exchanges, security researchers, and on-chain investigators. Circle and Tether have already frozen approximately $320,000 in stablecoins linked to the attacker’s address, in coordination with Bitget. That number needs context: $320,000 represents a fraction of a percent of the total declared loss.
The Withdrawal Schedule
Bitget published a detailed, asset-by-asset timeline for the gradual resumption of withdrawals, designed to manage liquidity and avoid sudden pressure on the network. Bitcoin withdrawals restart on September 28 at 08:00 UTC, followed by Ether on September 29 and USDT across multiple supported networks on September 30. All remaining assets, including any recoverable XRP, along with remaining services, are expected to follow by October 2. CEO Gracy Chen will also hold a public Q&A session thirty minutes before Bitcoin withdrawals reopen, to brief the community directly on the state of the investigation.
Bitget says the vulnerability exploited by the attacker has been identified and patched. The exchange confirmed its earlier account: the attack compromised a backend infrastructure system, making fraudulent transfers appear authorized without private keys ever being exposed. On attribution, the CEO stated that IP addresses consistent with VPN services previously used by a North Korea-linked group were detected. That remains a company-stated suspicion, not an independently confirmed attribution. The investigation is formally still open.
Withdrawal Schedule
Gradual reopening, asset by asset. Source: Bitget, September 26, 2026
- September 28, 08:00 UTC: Bitcoin withdrawals reopen.
- September 29-30: Ether and USDT across multiple networks follow.
- By October 2: all remaining assets and services.
Why Ripple Cannot Simply Freeze the Stolen XRP
The third development is the most technically significant. The attacker moved approximately $83 million in stolen XRP out of three of the five wallets where the funds had originally been split, leaving around $75 million still sitting in the original accounts. The core issue is structural, not a policy choice. A centralized stablecoin issuer like Circle or Tether can block tokens it has issued directly, on request. The XRP Ledger protocol contains no mechanism that would allow Ripple to unilaterally freeze native XRP held in a wallet controlled by the attacker. Exchanges can restrict accounts that receive those XRP once deposited with them, but there is no way to block the funds while they remain in the original wallet.
The same logic applies, for structurally parallel reasons, to the more than 63,000 Ether also stolen, worth approximately $183 million at the time of the attack. Ether is a native blockchain asset, not a token issued by a company, so no issuer holds the power to freeze it. The comparison is useful because it clarifies a distinction that often gets blurred: some digital assets have an emergency “off switch” controlled by a corporate issuer; others, by design, do not, regardless of how serious the circumstances are.
A Hidden Risk Inside the Protection Fund
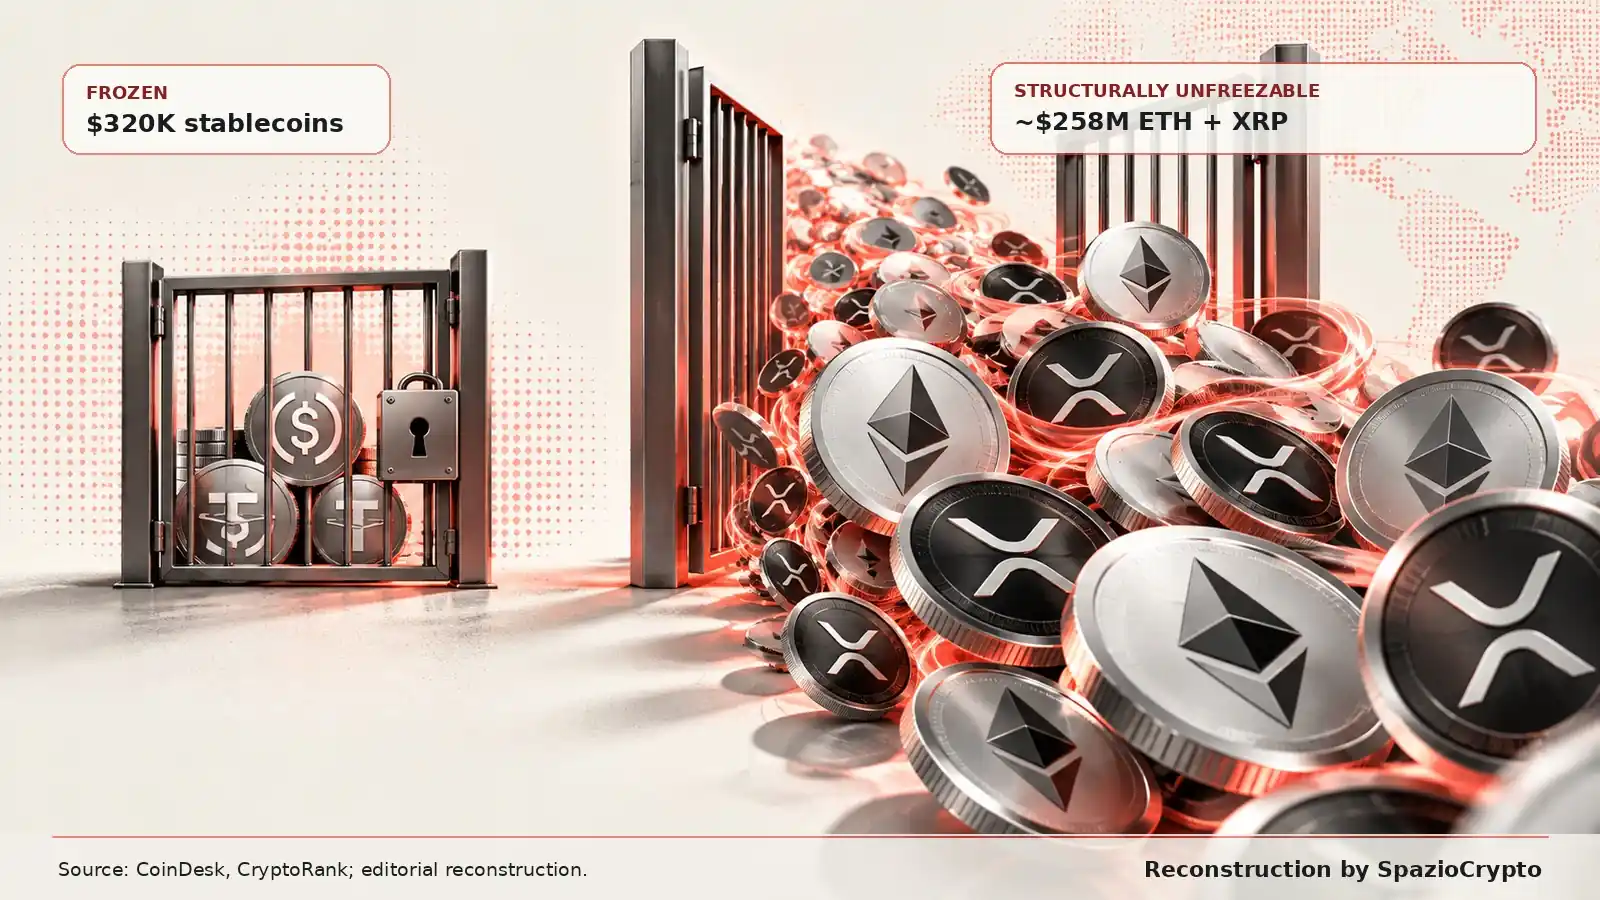
One detail that has received less attention concerns the composition of the fund Bitget uses to guarantee user reimbursement. The fund, established in 2022, holds 5,500 Bitcoin and is denominated entirely in a single volatile asset with no diversification into more stable currencies. At Bitcoin’s price of around $84,000 recorded on September 26, the fund was worth approximately $464 million, enough to cover 84% of the declared loss. But because the fund is Bitcoin-denominated, its coverage capacity moves with the asset’s price. A decline of roughly 16% from the September 26 price would push the fund below the threshold needed to cover the full declared loss, a risk that is separate from the cyberattack itself and not always visible in the exchange’s reassurances to users.
The Bigger Picture
This update illustrates how managing an attack of this scale unfolds across multiple layers at once, not in a neat sequence of separate phases. While the exchange communicates a recovery schedule and reassures users about financial coverage, the attacker continues moving assets on-chain in real time, and the security community must contend with the structural limits of certain protocols when it comes to freezing stolen funds. That theme connects to a broader conversation about the different types of crypto wallets and their respective risk profiles.
Two lessons emerge. First, Bitget’s operational transparency, with precise calendars and consistent updates on the real damage figure, offers a crisis-management approach worth acknowledging, especially compared to past incidents where information trickled out in fragments, as seen with the recent Fogo attack. Second, the protection fund being denominated entirely in Bitcoin is a reminder that even measures designed to reassure users carry their own risks, often less visible than the original threat but not trivial. SpazioCrypto will continue tracking both the attribution investigation and the fate of assets still moving on-chain.